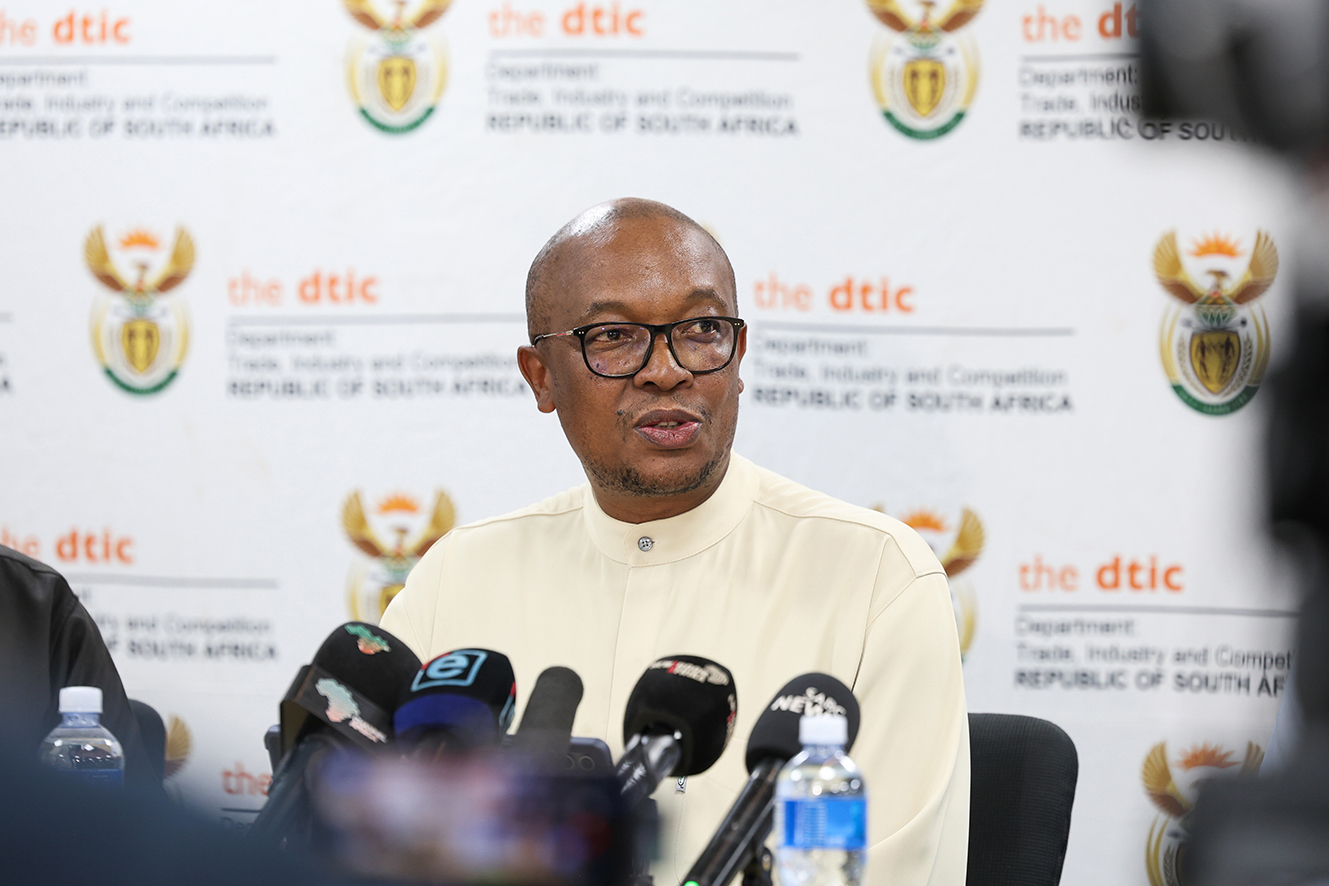
Members of Parliament have demanded that Trade, Industry and Competition minister Parks Tau urgently intervene after a parliamentary committee sharply criticised the leadership of the South African Bureau of Standards (SABS).
This comes after the members of parliament rejected the organisation’s annual performance presentation, citing governance failures, poor financial performance and the absence of senior executives and board members from a key oversight meeting.
The portfolio committee on trade, industry and competition took aim at SABS after the standards body reported that it achieved only 10 of its 18 key performance indicators during the 2024/2025 financial year and posted a net loss of R24 million.
Committee members also questioned whether a November 2024 cyberattack was being used to explain broader operational weaknesses that predated the incident. By the end of the session, lawmakers resolved not to accept the report and announced plans for an urgent oversight visit.
Committee outraged by leadership absence
The strongest criticism centred on the absence of SABS board members and senior leadership from the parliamentary briefing. The presentation was led by officials, while acting CEO Blake Moseli-Fatula was reported to be on sick leave.
DA MP Toby Chance described the situation as “extraordinary”, saying there was “not a single board member” present and comparing the institution to a vessel whose leadership had “abandoned ship”. Other members echoed the sentiment, arguing that Parliament could not effectively hold the organisation accountable without its board and executive leadership in attendance.
Read more: Not all PPEs on the market are certified – SABS
Committee chairperson Lufefe Mkutu said lawmakers took a “serious exception” to the absence of both management and the board, describing SABS as a “delinquent institution” and questioning the effectiveness of its governance structures.
Cyberattack fails to convince MPs
Several MPs challenged SABS’s reliance on a ransomware attack suffered in November 2024 as the principal explanation for missed targets and financial underperformance. The attack encrypted business applications, data storage systems, backup systems and disaster recovery infrastructure, severely disrupting operations.
ANC MP Mzwandile Masina warned that the cyberattack should not become a “cover” for broader management shortcomings. He questioned whether SABS would have performed significantly better had the attack not occurred and argued that achieving only 10 of 18 targets remained unsatisfactory.
Read more: Safety standards for sanitary towels upgraded
Committee members further noted that the Auditor-General’s findings and security assessments had identified weaknesses in SABS’s IT controls and cybersecurity posture before the attack occurred. Those findings included unsupported operating systems, insecure network ports and inadequate protection of critical infrastructure.
Financial performance raises alarms
SABS told Parliament that total income rose 2.8% to R797 million during 2024/2025, but expenditure outpaced revenue, resulting in an operating loss of R69.5 million and a net loss of R24 million.
The organisation reported a negative operating margin of 10.4%, missed all three financial sustainability targets and achieved revenue growth of only 0.6% against a target of 5%. Paliamentarians expressed concern that commercial revenue remained largely flat while employee costs continued to drive expenditure higher.
Questions were also raised about whether SABS remains a viable long-term entity. MPs demanded greater disclosure around assets, liabilities, capital expenditure and future funding arrangements, arguing that Parliament had not been provided with a complete picture of the organisation’s financial health.
Stinging criticism of governance failures
The MPs repeatedly linked the cyberattack to broader governance weaknesses. MPs noted that SABS had been warned about shortcomings in safeguarding IT assets long before the ransomware incident and questioned why remedial action was implemented only after the attack occurred.
Read more: Bureau of Standards calls for South Africans to practice safe sex
One MP highlighted that a chief technology and digital officer was appointed only in 2026, nearly two years after critical vulnerabilities had been identified. Members also raised concerns about repeated Auditor-General findings and questioned why corrective actions had not been implemented sooner.
The committee further criticised SABS for delays in finalising its more recent financial statements. Members complained that Parliament was being asked to perform oversight using outdated financial information, with 2025/2026 audited results still not finalised.
Calls mount for intervention
By the conclusion of the meeting, MPs across party lines agreed that stronger intervention was needed. The committee resolved to write formally to Trade, Industry and Competition Minister Parks Tau and the department’s Director-General to express dissatisfaction with SABS’s performance and governance.
Parliament also directed SABS to submit a comprehensive accountability and turnaround report within 30 days. The report is expected to cover cybersecurity investigations, financial recovery plans, accreditation restoration efforts, governance reforms and the institution’s industrial impact.
Members further called for urgent filling of leadership vacancies, including the appointment of a permanent chief executive.
Oversight visit planned
The committee announced that it would conduct an urgent oversight visit to SABS headquarters and insisted that the entire board and executive management team attend a future accountability session in person.
ANC parliamentarian Lufefe Mkutu said the current presentation would effectively be put “on ice” until Parliament had the opportunity to engage directly with the organisation’s leadership. He added that lawmakers needed to establish whether the board was actively exercising oversight and whether current management had the capacity to turn the institution around.
Responding to the criticism, DTIC Director-General Simphiwe Hamilton acknowledged the committee’s concerns, apologised for the shortcomings identified during the meeting and committed the department to preparing for the planned oversight intervention.
SABS defends recovery efforts
Despite the backlash, SABS executives argued that the 2024 cyberattack had fundamentally disrupted operations for nearly five months of the financial year. Management said extensive recovery work had been undertaken, including network segmentation, firewall upgrades, implementation of new ERP systems, appointment of cybersecurity specialists and development of a new cybersecurity strategy.
The organisation also reported progress in restoring critical systems and strengthening disaster recovery processes. However, those assurances did little to calm committee concerns, with MPs insisting that Parliament needed direct answers from the board and senior leadership before accepting that the institution was on a credible recovery path.
- Members of Parliament have demanded that Trade, Industry and Competition minister Parks Tau urgently intervene after a parliamentary committee sharply criticised the leadership of the South African Bureau of Standards (SABS).
- This comes after the members of parliament rejected the organisation’s annual performance presentation, citing governance failures, poor financial performance and the absence of senior executives and board members from a key oversight meeting.
- The portfolio committee on trade, industry and competition took aim at SABS after the standards body reported that it achieved only 10 of its 18 key performance indicators during the 2024/2025 financial year and posted a net loss of R24 million.
- Committee members also questioned whether a November 2024 cyberattack was being used to explain broader operational weaknesses that predated the incident.
- By the end of the session, lawmakers resolved not to accept the report and announced plans for an urgent oversight visit.